4Cyber GRC
Know what applies. See the gaps. Put compliance into action.
4Cyber analyzes your company’s information to identify applicable regulatory requirements, assess compliance gaps, and prepare an implementation plan tailored to your business.
Upload your documentation or connect supported business systems. AI uses that context to create and update company-specific policies, recommend corrective actions, and route proposed changes for approval, all in one platform.
- SOC 2
- NIST CSF
- HIPAA
- CMMC
- GapClosed
Framework coverage
Framework coverage 78 %
Regulatory Applicability
Start by understanding which requirements apply to your business.
Your industry, operations, data, and business relationships shape your compliance obligations.
4Cyber analyzes the information you provide and data available through supported connections to identify relevant legal and regulatory requirements within its supported coverage.
Give your team a company-specific starting point for reviewing obligations and planning implementation.
Gap Analysis
See where your company stands against each requirement.
Turn uploaded documents and connected business information into a structured compliance assessment.
4Cyber evaluates the available information against identified requirements, highlights gaps and inconsistencies, and identifies where further information or evidence is needed.
Understand what is documented, what needs improvement, and what your team should address next.
- Requirements relevant to your organization
- Findings based on your documents and available system data
- Missing or inconsistent policies and procedures
- Areas requiring additional information or evidence
- Recommended actions to address identified gaps
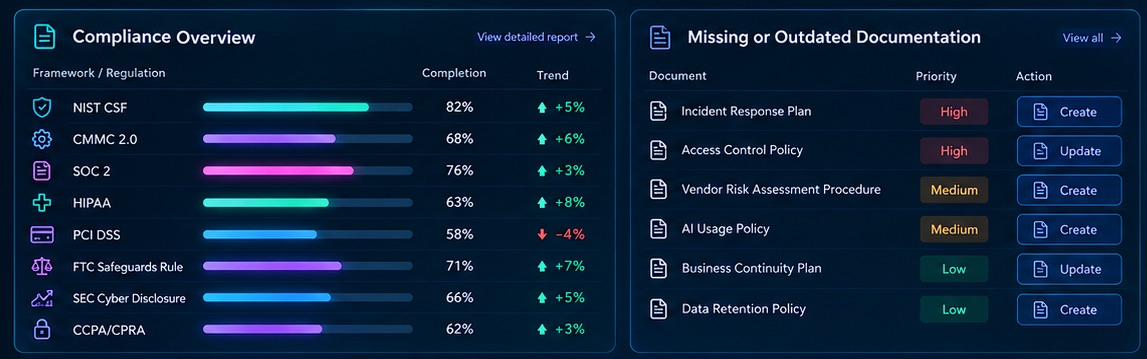
Company-Specific Documentation
Compliance documentation built around how your company works.
Create policies and procedures that reflect your organizational structure, systems, processes, and responsibilities.
4Cyber uses your company’s information and assessment findings to draft missing documentation and revise existing documents. Proposed changes move through review and approval before becoming part of your operating policies.
Create what’s missing
Prepare company-specific drafts to address documentation gaps.
Update what you already have
Revise existing policies and procedures to reflect relevant requirements and your current operations.
Keep the details connected
Align documentation with the teams, responsibilities, and processes recorded in the platform.
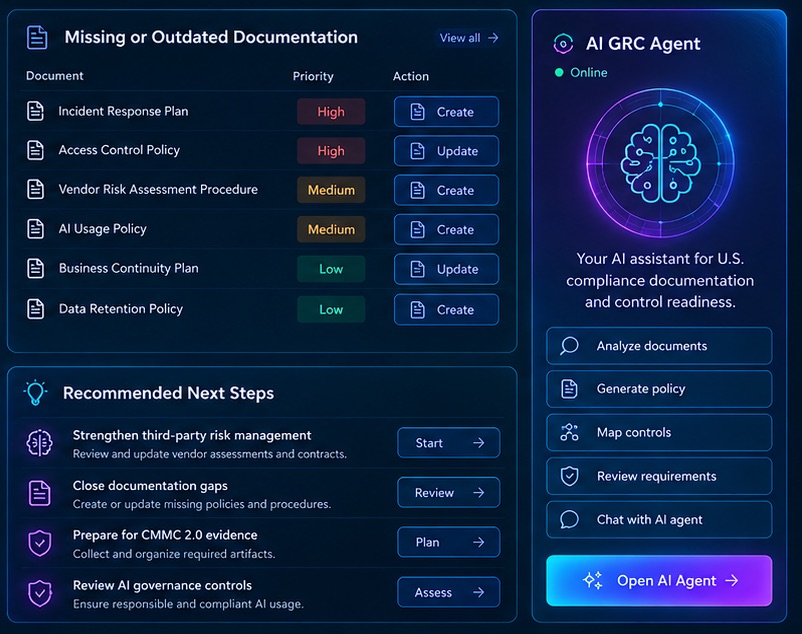
Implementation
Turn your assessment into a managed implementation process.
Move from identified gaps to concrete work.
4Cyber prepares recommended corrective actions and supporting documentation, routes proposals for approval, and helps your team manage implementation through assigned responsibilities and deadlines.
Track progress and keep evidence of completed work connected to the requirements it supports.
One workflow from assessment to documentation, approval, and follow-through.
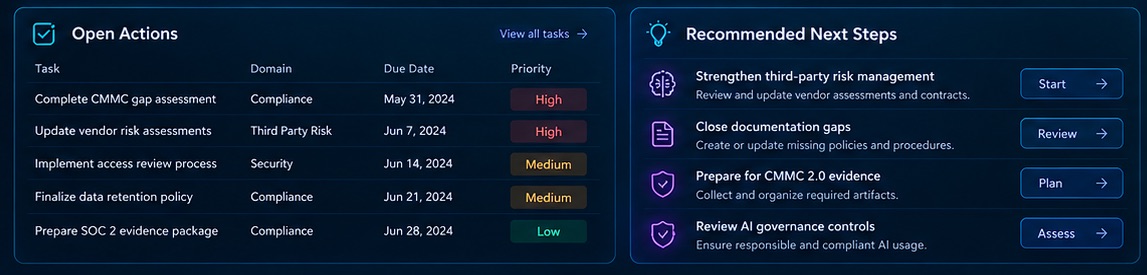
Business & Regulatory Change
Keep compliance aligned with your changing business.
A new system, an updated process, or a change in responsibilities can affect your compliance position.
As changes are recorded in 4Cyber or received through supported connections, the platform reassesses affected requirements and identifies potential gaps.
AI prepares relevant document updates and follow-up recommendations, then sends them to the appropriate reviewers for approval.
Regulatory change management
Review updates to the regulatory sources covered by your compliance program. Assess which policies and activities may be affected, then manage the resulting recommendations, approvals, and implementation work in 4Cyber.
Review and approval
Keep your team in control of compliance decisions. Route proposed changes to responsible reviewers and keep a clear record of what was proposed, approved, and implemented.
See what changed, understand the impact, and manage the response.
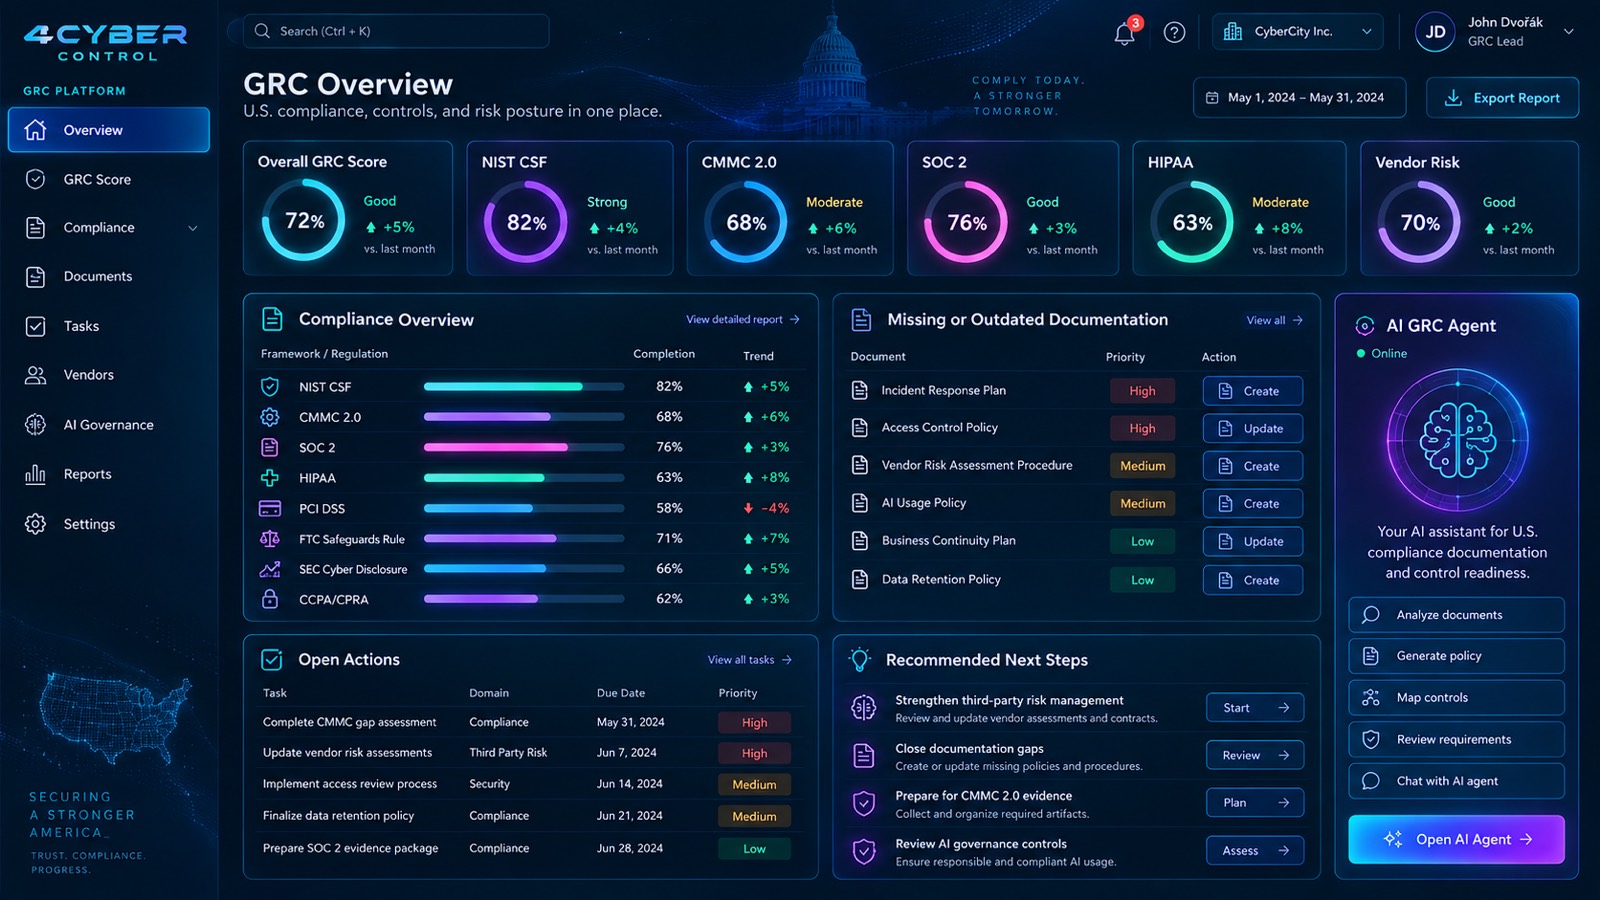
Shared Overview
See what applies, what is missing, and what happens next.
Bring obligations, findings, documentation, approvals, and implementation progress into one shared view.
For compliance teams
Understand the assessment findings and coordinate the work needed to address them.
For responsible teams
See assigned actions, related requirements, and the documentation supporting implementation.
For leadership
Review open gaps, pending decisions, and progress across the compliance program.
From company data to ongoing compliance management.
- 01
Build your company context
Upload existing documentation or connect supported business systems.
- 02
Identify relevant obligations
AI analyzes your company information to identify applicable requirements within the platform’s supported coverage.
- 03
Assess the gaps
Review findings based on your documentation, available system data, and identified requirements.
- 04
Prepare the implementation
Generate company-specific document drafts, update existing policies, and prepare corrective actions.
- 05
Review, approve, and implement
Route proposals to responsible reviewers, assign the work, and track completion.
- 06
Keep the program current
Reassess changes and manage follow-up actions as your organization and relevant requirements evolve.
Frequently asked questions
How does 4Cyber identify which requirements apply?
4Cyber analyzes the company information you provide and data available through supported system connections. It uses this context to identify relevant obligations within its supported regulatory coverage for your team to review.
Can we use our existing documentation?
Yes. Upload your existing policies and procedures so 4Cyber can assess them, identify gaps, and prepare targeted revisions.
Are the generated documents specific to our company?
Yes. Drafts are prepared using your company’s information, organizational structure, processes, and assessment findings. Your team reviews and approves proposed documents and changes.
What happens after the gap analysis?
4Cyber prepares recommended actions and supporting documentation, then helps manage approval, assignment, implementation, and progress tracking in the same platform.
Can 4Cyber work with data from our systems?
Yes, through supported connections. Available integrations and accessible data determine which information can be included in the assessment.
Does the platform automatically make our company compliant?
4Cyber supports identification, assessment, documentation, and implementation. Your team remains responsible for reviewing recommendations, implementing operational and technical controls, and providing accurate information.
4Cyber GRC
See a compliance plan built around your business.
Explore how 4Cyber uses company information to identify relevant requirements, assess gaps, and prepare tailored documentation and implementation actions.